 ComingUp
CyberShield – Windows Ransomware Protection
Windows agent that detects ransomware and freezes it in ~1 second. Full IP.

Is this your project? Ask us to take it down
Gallery
About
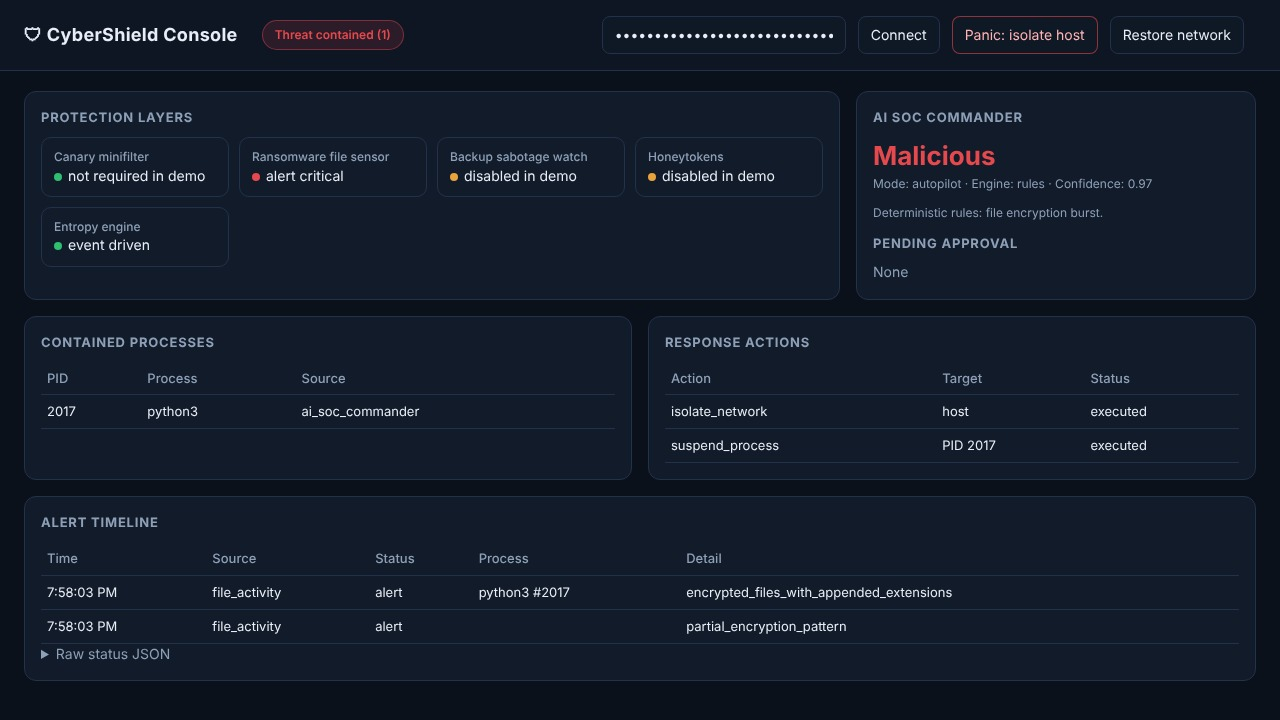
CyberShield is a Windows ransomware early-warning and response agent. It catches ransomware while it is encrypting, identifies the process doing it, freezes it in about a second, and cuts the machine off the network before the attack spreads.
How it works
• Reads the files themselves: headers that no longer match their type (a PDF that is no longer a PDF), text that turns random, ".docx.locked" style renames, and ransom notes
• Raises an incident only when several files change this way within seconds, so normal work doesn't trigger it
• Identifies the responsible process by correlating its disk writes with the changed files
• Suspends that process and isolates the host, keeping chosen management ports (e.g. RDP) open
• Extra tripwires: kernel canary minifilter (decoy file), backup-deletion watch, honeytoken files
• Decisions by a deterministic rules engine; an optional local AI advisor; every action passes a policy check
Tested results
• Simulated ransomware stopped in about 1 second, attacker process correctly identified
• Zero false alarms on 345 everyday files (Office, photos, PDFs, zip archives, downloads)
• 74 automated tests + a one-minute verification scorecard the buyer can run
What you get
• Full Python and C++ source code and exclusive IP transfer
• Kernel minifilter source with free build (GitHub Actions) and test-signing scripts
• Offline license engine to sell it to your own customers
• Boot-time agent, installer script, operator dashboard
• RDP brute-force protection module (Windows Firewall bans)
• Full due-diligence documents: architecture, build/signing guide, asset manifest, verification record
• 30 days of support and handover calls
Honest notes
Protection works without the kernel driver. To ship the driver to customers, it needs Microsoft signing (the buyer's step). No customers or revenue yet: this is a ready product for a security company or MSP that wants a ransomware offering without building it from scratch.
Comments (0)
No comments yet. Be the first to comment!
Related Products
Reswardo — Bóveda privada para tu legado digital
Reswardo — Production-ready encrypted digital legacy and continuity SaaS
SteelSuit
External web security scanner: TLS, headers, secrets & CVEs

Ad Blocker
FormCrab.com
Get messages while you hide your email
XCloak
MyVault — Personal Command Center
All-in-one personal vault for passwords, files, bills, and expenses.